By Coulée Raphaël
- 1
These comparisons help perceive the differences between various cryptographic algorithms and safety concepts used in real-world systems. Such methods had been used earlier than fashionable computers., mainly use substitution and transposition methods to hide the original message. This type of cryptography isn’t particularly related to anyone exterior of the cyber-security field. To safely change encryption keys with an unknown particular person, a key change algorithm similar to Diffie-Hellman is utilized.
In essentially the most general phrases, a brute drive attack is a method of trial and error that attempts all potential password mixtures. This technique works properly for brief passwords, but it takes a very lengthy time to try all potential passwords. When attackers have matching plaintext and encrypted ciphertext samples, they analyze patterns to deduce encryption keys or algorithms.
Symmetric Key Cryptography (secret Key)
Transactions are secured using public-key encryption, and blockchain uses cryptographic hashes to make sure nobody can tamper with the data. Some frequent hash algorithms embody SHA-256, which produces a 256-bit hash worth, and MD5, which produces a 128-bit hexadecimal number. Hash capabilities are extensively used in password storage, file integrity checks, and blockchain security.
Weak Keys
- Only those who have a bit of code generally identified as a “key” can “unlock” the data and entry the data in a non-scrambled form.
- Next-generation superior protocols like quantum cryptography and elliptic curve cryptography (ECC) represent the cutting edge of cryptographic strategies.
- As organizations digitize rapidly around cloud, cell, and IoT technologies, cybersecurity hinges greatly on advancing uses of cryptography for securing these rising digital attack surfaces and workloads.
- Whether Or Not sender or recipient, all events concerned should have entry to the identical key.
- Keys should be created with a high-quality, licensed random quantity generator that collects entropy—the info density of a file in bits or characters—from suitable hardware noise sources.
A frequent cryptography definition is the apply of coding info to make sure solely the individual that a message was written for can learn and course of the information. This cybersecurity apply, also referred to as cryptology, combines varied disciplines like laptop science, engineering, and mathematics to create complicated codes that hide the true that means of a message. As everyone knows that cryptography method is use to transform plain textual content into ciphertext. Mainly cryptographic key’s a string of characters which is used to encrypts the data and decrypt the information. In quick, cryptography builds the trust we want to operate in a digital society, quietly working in the background to maintain things secure, private, and dependable. Asymmetric-key cryptography has an advantage over symmetric-key cryptography because you needn’t share the necessary thing beforehand.
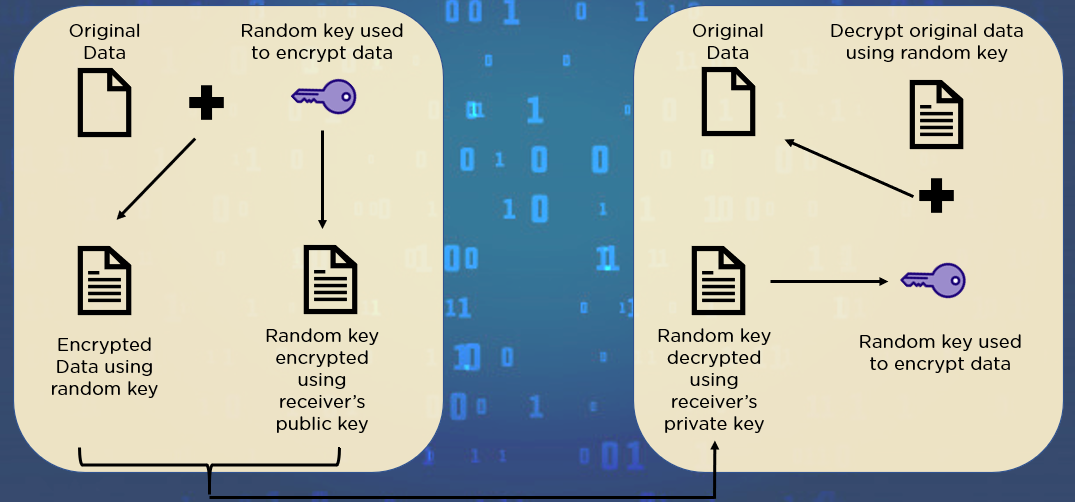
Aes (advanced Encryption Standard):
This makes hashing algorithms a fantastic software for guaranteeing knowledge integrity. Upon receiving the message, you can run the identical hashing algorithm on the message textual content; if the hash you produce is totally different from the one accompanying the message, you know the message has been modified in transit. You could recognize a few of these rules from variations of the CIA triad. The first of these makes use of is the apparent one—you can maintain data https://remedyalliance.com/chinese-govt-hackers-exploiting-new-atlassian-vulnerability-microsoft-says.html?noamp=mobile secret by encrypting it. The others take a bit of explanation, which we’ll get into as we describe the several sorts of cryptography. Cryptography is necessary for securing digital communication, protecting sensitive data, and guaranteeing on-line privateness.
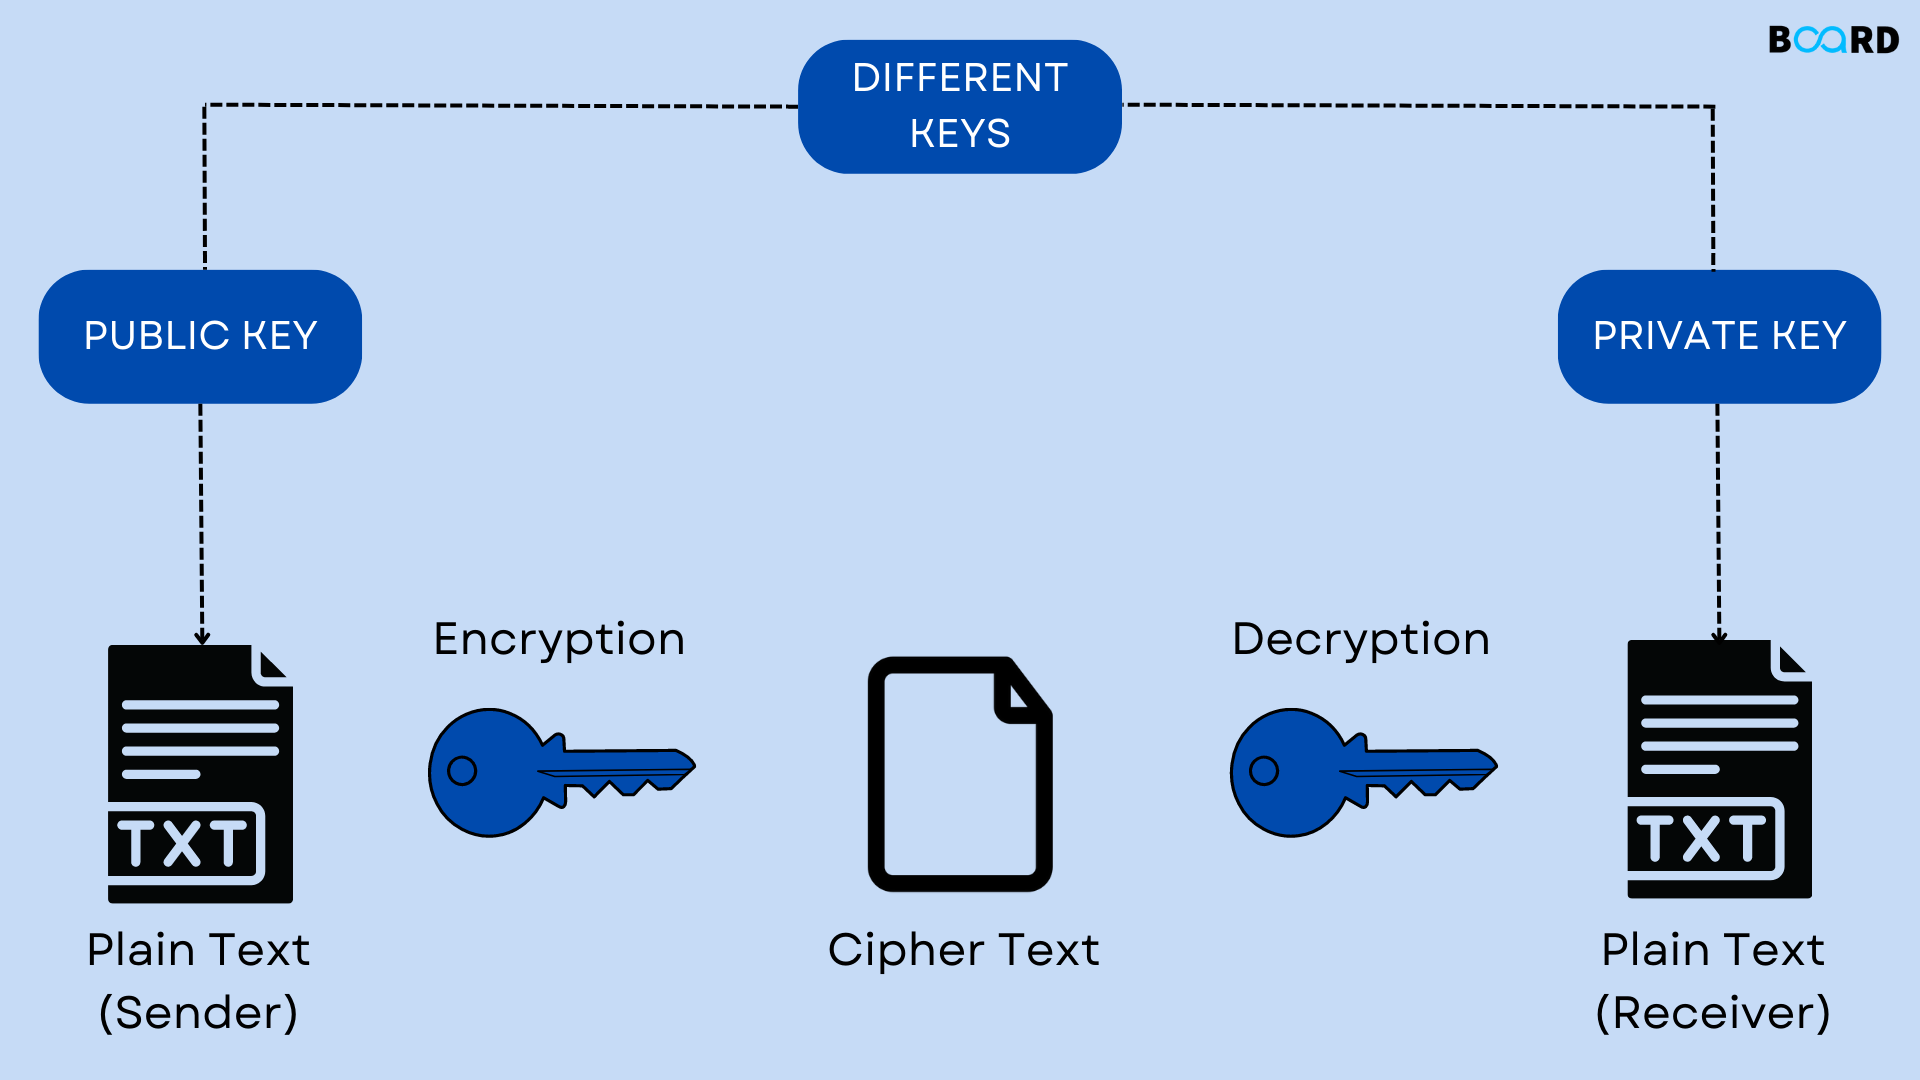
Uneven cryptography (also known as public key cryptography) makes use of one personal key and one public key. Data that’s encrypted with a public and private key requires each the public key and the recipient’s personal key to be decrypted. For example, in symmetric encryption, Alice and Bob both have the same key. Alice locks the message (encrypts it) and sends it to Bob, who unlocks it (decrypts it) using that very same key. Only Bob’s personal key can decrypt it, so even when somebody intercepts it, they can’t unlock it with out that personal key. The Caesar cipher is amongst the https://curewright.com/chinese-govt-hackers-exploiting-new-atlassian-vulnerability-microsoft-says.html earliest known encryption strategies, named after Julius Caesar, who used it to guard his navy communications.


